Cloud · AI agent securitySeptember 18, 20264 min · updated September 21, 2026
AWS proposes isolated MicroVMs for self-hosted AI agents
Rephrased by Daillac
Source: AWS ↗D
In brief
- AWS presents a self-hosted control plane that launches one MicroVM per agent session.
- Isolation covers the kernel, filesystem and network namespace.
- Network egress and secret controls remain architecture decisions.
Isolate where the agent acts
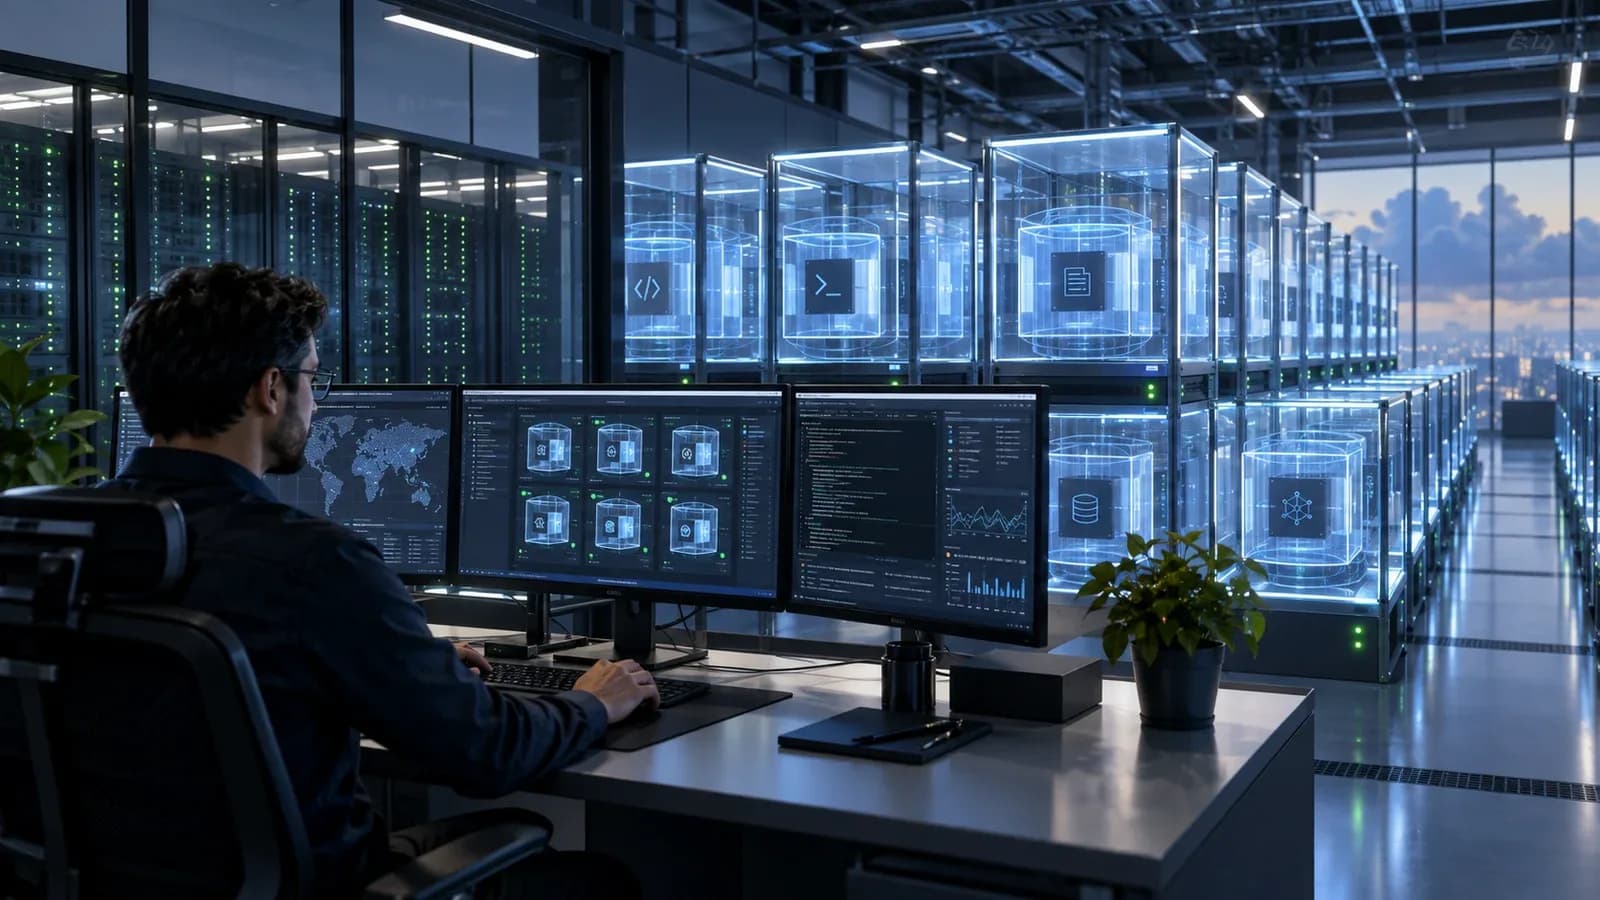
The AWS pattern creates an ephemeral environment for each session while keeping orchestration in the customer account. Separation limits the blast radius of faulty generated code, a compromised tool or prompt injection.
1 session
isolated per session reduces shared state and blast radius.
Source : AWS
What this changes for an organization
A sandbox is only one layer. Combine it with least privilege, short-lived credentials, an explicit network allowlist and useful logs. An isolated MicroVM that can still reach all production systems remains dangerous.
Four controls to put in place
- Create a fresh environment per session or sensitive task.
- Mount only required data and use read-only access where possible.
- Block network access by default, then allow required destinations.
- Destroy secrets and the environment when the session ends.
What this announcement does not establish
Virtual-machine isolation reduces blast radius, but it cannot stop an authorized agent from sending data to an allowed destination or using an overly powerful secret. The threat model must include the control plane, base image, dependency chain and reachable services.
TableDecision framework · shareable block
| Avoid | Do | |
|---|---|---|
| 01 | AWS presents a self-hosted control plane that launches one MicroVM per agent session. | Create a fresh environment per session or sensitive task. |
| 02 | Isolation covers the kernel, filesystem and network namespace. | Mount only required data and use read-only access where possible. |
| 03 | Network egress and secret controls remain architecture decisions. | Block network access by default, then allow required destinations. |
Practical questions
What exactly does the primary source announce?+
The AWS pattern creates an ephemeral environment for each session while keeping orchestration in the customer account. Separation limits the blast radius of faulty generated code, a compromised tool or prompt injection.
What is a reasonable first action?+
Create a fresh environment per session or sensitive task. Mount only required data and use read-only access where possible.
Which limitation should remain in view?+
Virtual-machine isolation reduces blast radius, but it cannot stop an authorized agent from sending data to an allowed destination or using an overly powerful secret. The threat model must include the control plane, base image, dependency chain and reachable services.
How should implementation be monitored?+
Block network access by default, then allow required destinations. Destroy secrets and the environment when the session ends.
Turn this news into a concrete decision
DAILLAC can define the architecture, controls and measurements that fit your organization.
Sources & method
Article written from two primary sources, verified on September 21, 2026, then contextualized for Québec and Canadian organizations.
Read the original source: AWS ↗