Infrastructure · Digital sovereigntyAugust 25, 20263 min · updated August 27, 2026
Cisco launches sovereign critical infrastructure in Canada
Rephrased by Daillac
Source: Cisco ↗D
Written by
DaillacEditorial team — Architecture, AI and cybersecurity · Saint-Jérôme · Greater Montréal
In brief
- Cisco is selling a configurable portfolio in Canada for on-site deployments and, where needed, environments fully isolated from the Internet.
- The offer targets governments, finance, healthcare and other operators of critical infrastructure, among others.
- Sovereignty also depends on operators, keys, privileged access, contracts and audit evidence — not only on where the servers sit.
What Cisco is actually putting on the market
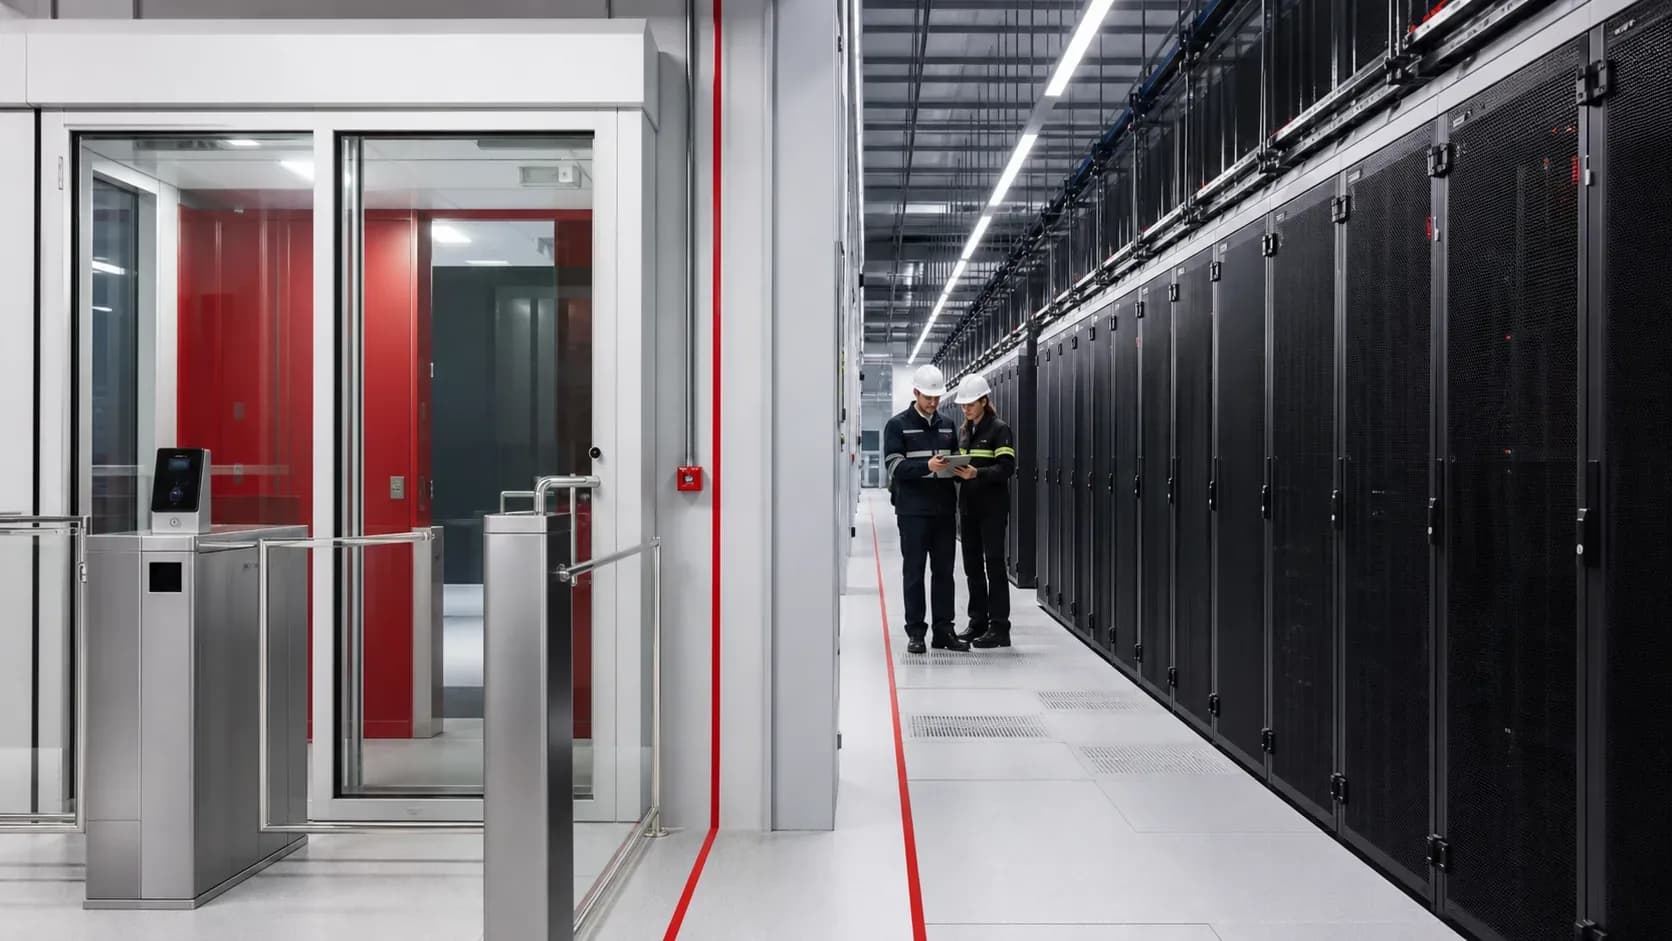
On August 25, Cisco announced the Canadian availability of its Sovereign Critical Infrastructure portfolio. In practice, it brings together networking, security, compute, collaboration and observability in a configuration that can stay within facilities owned and operated by the customer.
The air-gapped configuration draws the most attention. It lets the environment run without a permanent Internet connection. Cisco says it cannot remotely reach, control or disable products configured this way; operational responsibility then rests entirely with the customer organization.
100% on-site
The offer can be configured to run in the customer’s facilities, with no dependence on an external connection.
Capability announced by Cisco · the exact configuration depends on the project
Why the announcement comes now
The announcement lands as many organizations want to adopt AI without giving up control of their critical systems. For a bank, a hospital or a public body, a connectivity outage or an outside decision should not be enough to interrupt an essential service.
Cisco positions its portfolio as a foundation compatible with Canadian frameworks such as ITSG-33. The company also mentions FIPS 140-2 or 140-3 and Common Criteria certifications for most of its on-premises portfolio. These elements help an authorization process, but they are not automatically an authorization to operate.
TableTechnical promise and expected proof · shareable block
| Announcement | Buyer verification | |
|---|---|---|
| Isolation | Can operate in an air-gapped environment | Test every network exit, update and license dependency |
| Control | Operated under customer control | Document privileged accounts, support and emergency procedures |
| Compliance | Alignment with ITSG-33 and certifications | Link each control to the system, the risk and local evidence |
| Resilience | Less dependence on the public cloud | Plan for failover, spare parts, backups, patches and in-house skills |
What sovereign does not mean
Installing servers in Canada does not settle everything. You still need to examine vendor jurisdiction, the support chain, backups, telemetry, key ownership and how updates enter the environment.
- Accountability: who can approve a change, access a console or step in after an incident?
- Continuity: how long does the system stay fully operational without the vendor or the Internet?
- Evidence: which logs and reports show that the controls actually work?
- Reversibility: can data, configurations and workloads be migrated without excessive lock-in?
The architecture decision to make
Bringing everything on-site is not necessarily the right answer. A hybrid architecture can keep the most sensitive identities, data and functions in the sovereign environment, then leave less critical services in the cloud. Our guide to AI sovereignty in Canada explains the differences between residency, jurisdiction and operational control.
Turn the alert into a control plan
A sector alert is only useful if it changes an inventory, an access rule, a test or an incident procedure. The organization needs to identify the affected systems, their owner, the data they can reach and the actions a tool or account can really perform.
InfographicControl plan · shareable block
01
Reduce exposure
Remove unnecessary access, isolate environments and limit the secrets available.
02
Detect
Log sensitive actions, watch for deviations and keep the context needed for an investigation.
03
Respond
Name the decision-makers, test cutting off access and document how service is restored.
Prioritize by real impact
Fixes start with the systems able to expose information, change code or interrupt an operation. Likelihood alone is not enough: a rare but irreversible scenario may call for human approval or stronger technical separation.
Security questions
What is the first deliverable?+
A short inventory of the assets, owners, access, data and dependencies affected by the alert.
Is a written policy enough?+
No. It has to turn into technical controls, logs, tests and verifiable responsibilities.
What should be tested?+
Access revocation, detection, escalation, rollback and data recovery.
When should the analysis be redone?+
After a major change, a new tool, an incident, a critical vulnerability or a change of vendor.
Decide what really has to stay on-site
Not every workload carries the same risk. Let’s map the data, access and dependencies before choosing a sovereign or hybrid architecture.
Sources & method
Analysis of the official press release, put in context with Canadian guidance on IT risk and sovereign AI.
Read the original source: Cisco ↗News feed
October 18, 2026
Security · Automation
n8n security update: check your version and execution logs
October 18, 2026
AI · Costs and operations
Vercel groups AI Gateway logs by session: measure the full conversation
October 18, 2026
Security · Application testing