Cybersecurity · Cloud applicationsSeptember 9, 20264 min · updated September 21, 2026
Microsoft publishes a threat matrix for cloud web applications
Rephrased by Daillac
Source: Microsoft Security ↗D
In brief
- Microsoft organizes cloud application attack techniques using MITRE ATT&CK tactics.
- The matrix spans code, identities, deployments and connected resources.
- It can turn a technical audit into a prioritized security backlog.
A continuous view from application to cloud
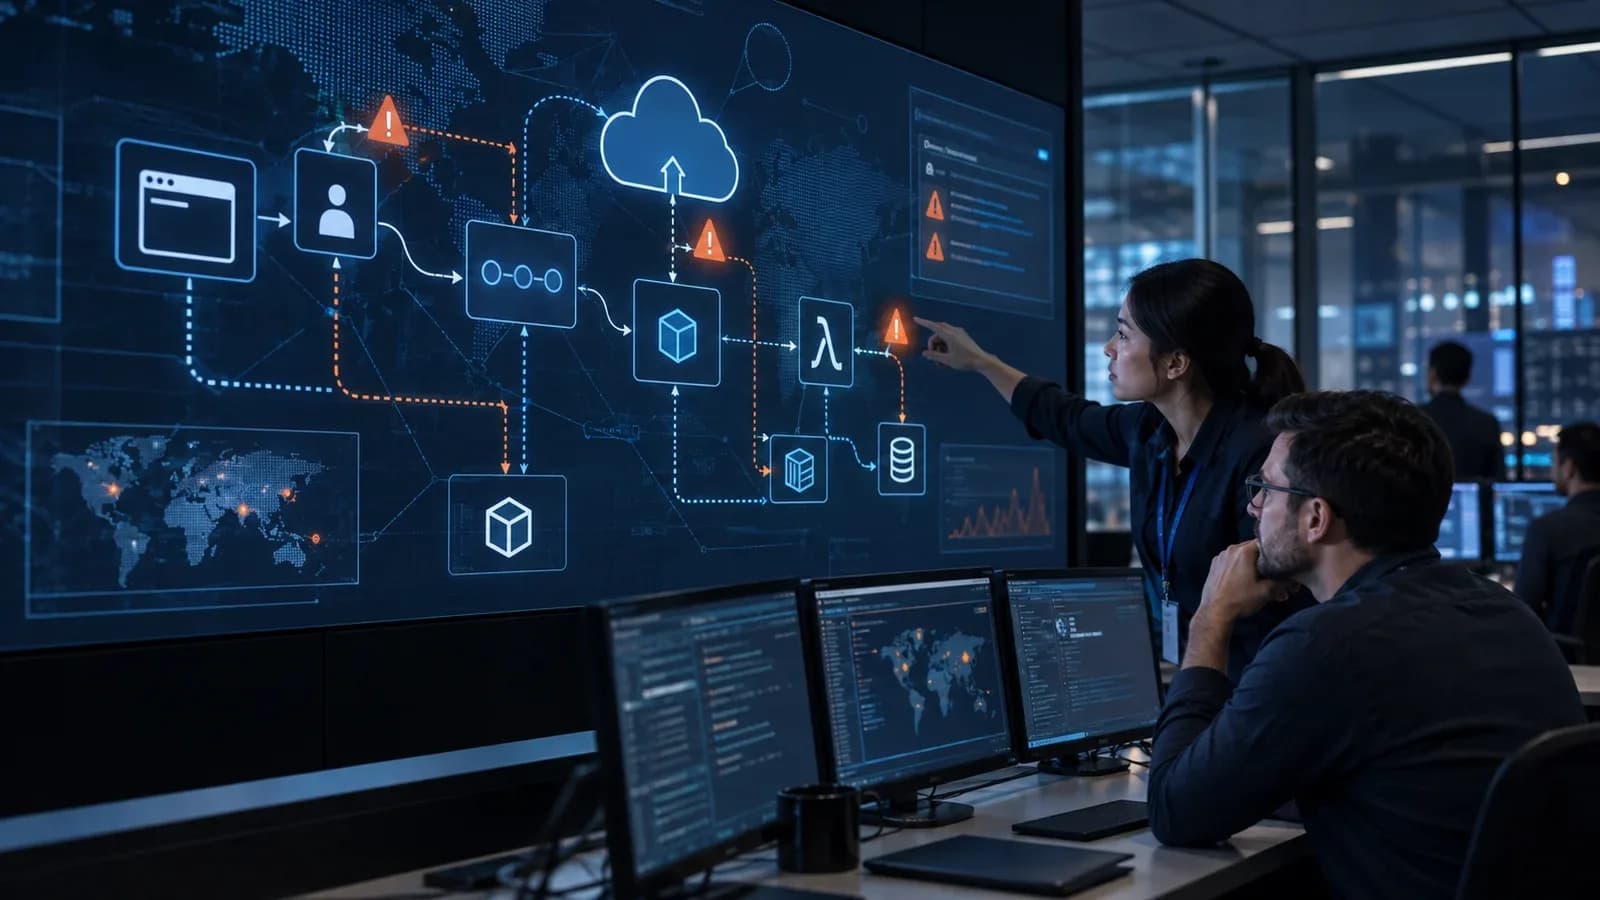
The matrix describes paths through application vulnerabilities, source repositories, container registries, administration interfaces, workload identities and databases. Assessing the application and platform separately can hide these chains.
11
tactics structure the matrix, from resource development through impact.
Source : Microsoft Security
What this changes for an organization
For a smaller organization, the matrix is most useful as a structured checklist. Start with exposed assets, runtime-accessible secrets and paths that can change production, then assign each risk an owner and remediation evidence.
Four controls to put in place
- Inventory public and administrative interfaces.
- Reduce workload identity privileges.
- Protect repositories, registries and pipelines with MFA and approvals.
- Test detection across one complete attack path.
What this announcement does not establish
A threat matrix organizes known scenarios, but it does not replace analysis of the actual architecture or code-specific vulnerability discovery. It can also create false confidence when a technique has a paper control without logs, testing or an operational owner.
TableDecision framework · shareable block
| Avoid | Do | |
|---|---|---|
| 01 | Microsoft organizes cloud application attack techniques using MITRE ATT&CK tactics. | Inventory public and administrative interfaces. |
| 02 | The matrix spans code, identities, deployments and connected resources. | Reduce workload identity privileges. |
| 03 | It can turn a technical audit into a prioritized security backlog. | Protect repositories, registries and pipelines with MFA and approvals. |
Practical questions
What exactly does the primary source announce?+
The matrix describes paths through application vulnerabilities, source repositories, container registries, administration interfaces, workload identities and databases. Assessing the application and platform separately can hide these chains.
What is a reasonable first action?+
Inventory public and administrative interfaces. Reduce workload identity privileges.
Which limitation should remain in view?+
A threat matrix organizes known scenarios, but it does not replace analysis of the actual architecture or code-specific vulnerability discovery. It can also create false confidence when a technique has a paper control without logs, testing or an operational owner.
How should implementation be monitored?+
Protect repositories, registries and pipelines with MFA and approvals. Test detection across one complete attack path.
Turn this news into a concrete decision
DAILLAC can define the architecture, controls and measurements that fit your organization.
Sources & method
Article written from two primary sources, verified on September 21, 2026, then contextualized for Québec and Canadian organizations.
Read the original source: Microsoft Security ↗